Services
Claremont Security serves firms entrusted with sensitive client data across the United States: a fixed-fee two-week review, then AI set up on the tools your team already uses, the written security plan and compliance work your rules require, and ongoing care.
More work done with AI, without putting client data at risk.
Which rules apply depends on the kind of business. The industries page sets them out for accounting, tax and law practices and the other sectors it covers. Who we work with →
Four steps. Every fee fixed and in writing before work starts.
- 01Estimate
Your numbers on one page
What one improvement is worth to your firm, what it takes, and how soon it pays back.
Fee none
- 02Assessment
Baseline Security Assessment
Two weeks, read-only. Every gap, and which AI tools you can use on client work today.
Fixed fee · credited in full against the engagement that follows, if it starts within 90 days
- 03Rollout
AI rollout, Copilot or Claude
Gaps closed highest risk first, file access fixed, the tool set up, and staff trained.
Fee fixed per engagement · engagements and fees
- 04Ongoing care
Kept current every quarter
As your staff, the IRS forms and the tools change, with questionnaires answered and a quarterly review.
Fee monthly · cancellable at renewal
Where firms usually start
The three categories
Who each one is for, what it needs from you, and what you get. Fixed fee wherever the scope is fixed.
AI in daily operations
Staff get AI in a setup you control.Our position for every tool: until the vendor commits to U.S.-only processing and the firm can show who reaches the data, client tax return information goes in only with each client's consent.
- Copilot shows a person exactly what that person could already open, so the permission work comes first, never after
- SharePoint and OneDrive checked against who should have what, before Copilot is switched on
- It is rarely the AI. It is the folder somebody shared with the whole firm three years ago and forgot
A list of everything that is over-shared, named by site and library.
- Microsoft commits to storing prompts and responses in the United States for U.S. tenants, not yet to running the AI only there
- Prompts and responses are not used to train the underlying models
- Staff see the warning while they are still typing, not in a report a month later
Labels and policies switched on, the vendor’s no-training terms checked and filed, and one page saying where your data can and cannot go.
- Help with daily drafting for everyone, the morning inbox in Copilot, and one tool for the work your practice does most
- Fixed output standards and a person's review. Nothing any of them writes sends itself
- Anything that has to go outside the tenant goes through the Clean Room, which is free
Each one set up for your firm, AI use logged where the plan carries it (Purview on Copilot, the Compliance API on Claude Enterprise), and one page per agent saying what it may do and what it must refuse.
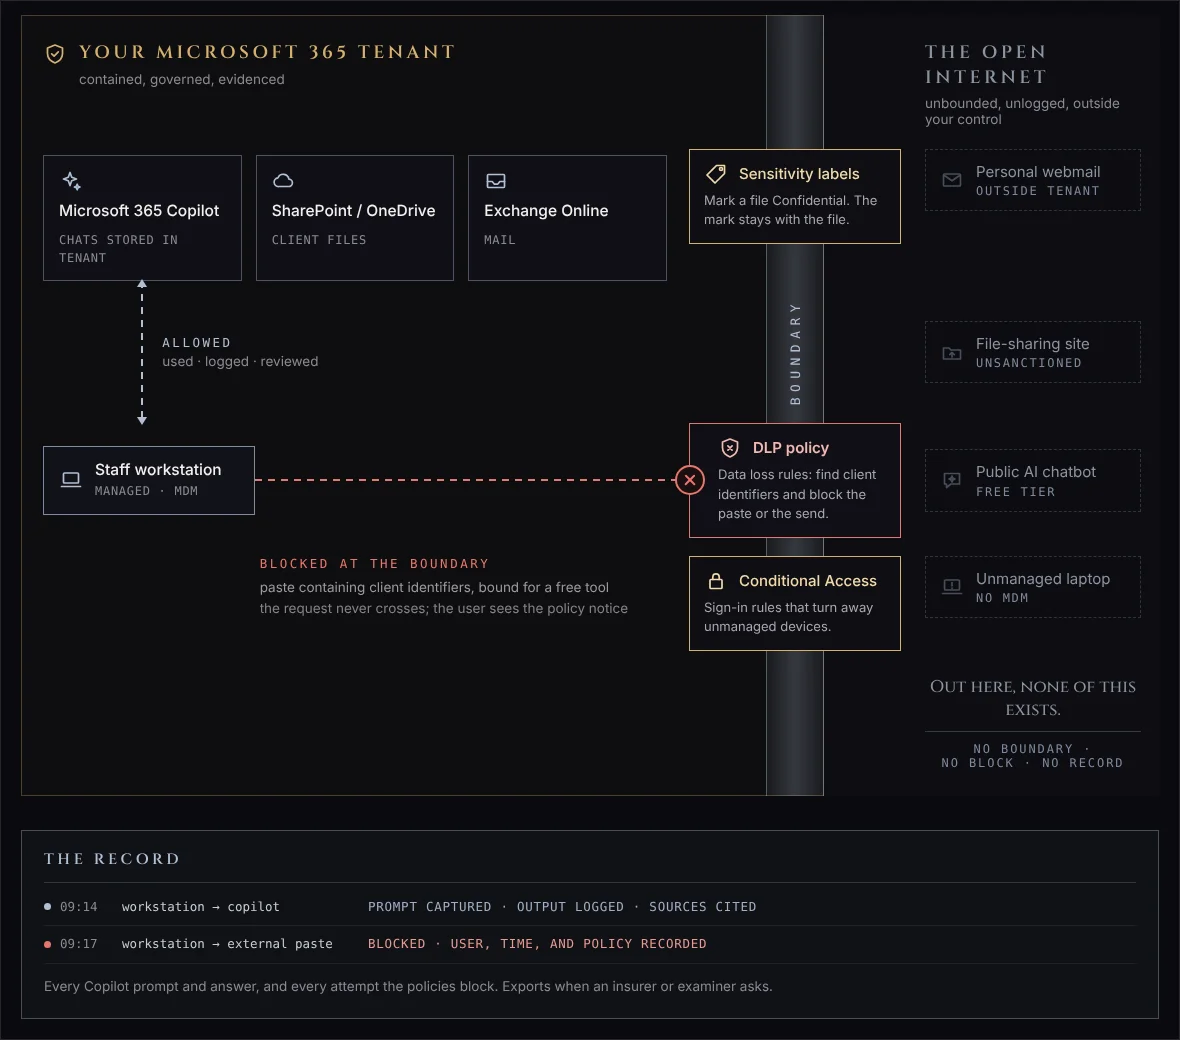 Where client data can go, and where it can'tOpen the diagram →
AI Oversight and Virtual CISO
Too small to justify a security hire.Too exposed to go without one. We lock down who can sign in, check what your existing tools actually cover, and answer for your security in writing.
- Multi-factor authentication on every account, the admin and service accounts included
- Those are the accounts that usually get an exemption, and the exempted group is where the real gap lives
- Offboarding runs from a written procedure rather than from memory
Sign-in rules switched on with every exemption written down, a register of who holds admin rights, and an offboarding checklist that cuts access on day one.
- On Business Premium you already pay for Defender. The work is proving it reaches every machine
- The problem is rarely a missed detection. It is the three laptops nobody knew were unmanaged
- Update status confirmed at the machine, not read off a dashboard
Defender set up to a written standard, coverage checked against your staff list, and update status confirmed machine by machine.
- Your AI setup kept current as the tools change
- One quarterly review with your leadership, with a short note on what changed in your AI tools and what to do about it. It is the only standing commitment.
Every control at deployment rather than held back for a higher tier, and a setup that improves instead of one frozen on the day it was built.
Compliance Documentation
A firm can be secure and unable to prove it.That gap is the exposure. We turn what you already do into the record a regulator expects to read.
- For firms that need proof, not just paperwork. Two weeks of looking from the day we get access
- Nothing is touched. Fixed fee, credited in full against the engagement that follows, if it starts within 90 days
- This is step 02 of the engagement above, not a second purchase
A list of every gap against 16 CFR Part 314 and IRS Publication 4557, each with an owner by role and a date. Plus which AI tools your firm can use on client work today, and what each needs first.
- For firms using an AI tool, or sending returns to preparers outside the United States
- We list what your client consent form must mention for each AI tool you use
- The wording itself comes from your lawyer or your tax software
What your client consent page must name for each provider, including anyone outside the United States who may receive or view return information, its support staff included. For Form 1040 clients the Social Security number stays out even with consent.
What we do not do
Stated plainly, because the gap between what a firm needs and what an outside advisor can deliver is exactly where engagements go wrong.
The platform monitors continuously. We review and respond to alerts on a defined business-hours cadence. We do not run a help desk or an around-the-clock response team. For overnight cover you need a managed detection provider, and we'll say so.
Category II is oversight and evidence. Known-exploited vulnerabilities are surfaced and tracked to closure with per-endpoint evidence, and your IT provider does the deploying.
Formal opinions and sign-offs belong to licensed firms. Claremont performs assessments and writes documentation you can hand to whoever asks.
No platform for it is in place. If that is a requirement, say so early and we will tell you who does it.
Two simultaneous engagements is the honest ceiling. If the calendar is full you will be told, not queued quietly.
How the function is structured from outside, what it covers, the cadence it runs on and what it runs on. The fractional model brief →
Start with a one-page estimate, or run the AI Exposure Check on your own tools and send us what it shows.
Get a one-page estimate Talk to us Run the instrumentSecurity or compliance team at a larger organization, or a firm subcontracting work: enterprise and partner engagements.